Windows Autopilot gave organisations another way to set up new laptops. Alongside custom software images applied before delivery, IT teams can now configure policies and apps in Microsoft Intune and let each device set itself up when it first connects.
What Autopilot does not change is the physical work. Devices still have to be received, checked, registered, labelled, packed and delivered to the right person at the right site. This guide compares the Autopilot routes available in 2026, explains what pre-staging means now, and sets out where each approach leaves work for your team.
What Is Windows Autopilot?
Windows Autopilot is Microsoft's cloud-based way to set up new Windows devices. A user signs in during the out-of-box experience, the device joins Microsoft Entra ID, enrols in Intune and installs the apps and policies assigned to it. No image needs to be applied before delivery.
Classic Autopilot needs each device to be registered with the service first. Registration links the device's hardware hash to your tenant. Microsoft says this is ideally done by the OEM, reseller or distributor at the point of sale. Manual registration is possible, but it requires booting each device into Windows to capture its hash, and Microsoft positions it mainly for testing and evaluation.
The Three Ways a Device Can Reach a User
Autopilot now covers three practical routes for new laptops. The difference that matters most to IT teams is where the setup time falls.
Autopilot user-driven. The user unboxes the device, signs in and waits while device and user apps install. It is the simplest model, but a slow network or a large app set means a long first morning.
Autopilot pre-provisioned. Formerly known as white glove, this splits setup into two phases. In the technician phase, run by the IT department, an OEM or a reseller, device-targeted apps and policies install before the device is resealed and shipped. The user then signs in and only user-targeted settings remain. Microsoft's pre-provisioning requirements include TPM 2.0 with device attestation, a supported Pro, Enterprise or Education edition and an Intune subscription. Virtual machines are not supported.
Autopilot device preparation. Microsoft's newer approach removes the need to register hardware hashes. It supports Windows 11 and Microsoft Entra join only, installs up to 25 essential apps and 10 scripts during setup, and reports progress in near real time. According to Microsoft's comparison of the two solutions, it does not yet support pre-provisioning, self-deploying mode or hybrid join.
What Pre-Staged Deployment Means Now
"Pre-staged" has meant different things over the years, which is why it causes confusion in procurement conversations. In practice it covers three approaches.
- Custom software imaging. A configured image with your applications, settings and security baseline is applied to each device before delivery. It fits specific application sets or configuration standards, sites with limited bandwidth, and fleets not managed through Intune.
- Autopilot pre-provisioning. Intune installs device-targeted apps and policies in a technician phase, then the device is resealed. It fits large app sets, slow sites, and executive or frontline devices that must work on arrival.
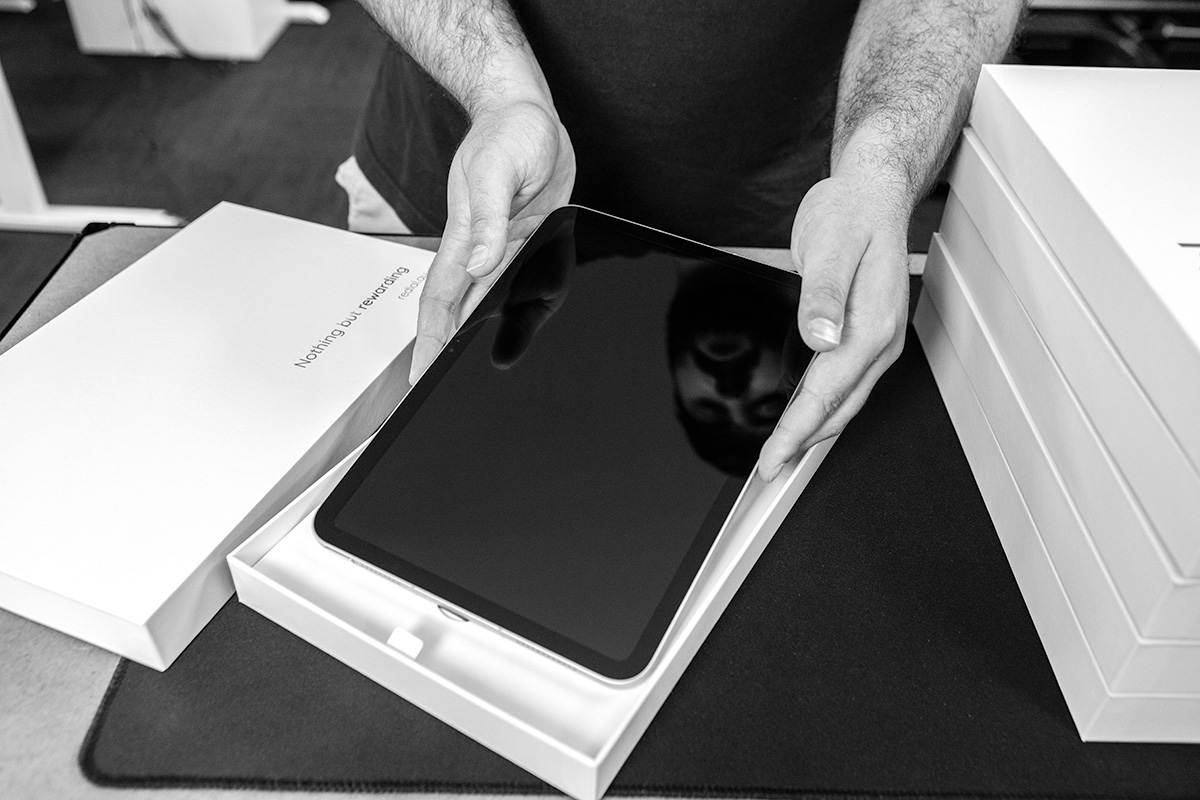
- Physical pre-staging. Devices are received, checked, registered, tagged and packed before shipping, whatever the software method. Every rollout needs it, including fully cloud-based ones.
Custom imaging and cloud provisioning are both valid approaches, and many organisations use both across different device groups. The right choice depends on how your environment is managed, which applications must work on day one and where devices are going. Canopy's Deploy service applies custom configurations and software images to your specification, and handles the physical staging around whichever approach your IT team or MSP uses.
Physical pre-staging is the work most often underestimated. Even a perfectly configured Autopilot tenant needs someone to unbox hardware, confirm serial numbers, check that registration has landed, apply asset tags, add peripherals and get each device to the right person. We put numbers to that effort in the hidden cost of device deployment.
Which Autopilot Route Fits Your Rollout
Three questions settle the choice for most organisations. A yes to any of them keeps you on classic Windows Autopilot for now.
- Do new devices need Microsoft Entra hybrid join? Device preparation supports Entra join only.
- Should devices be prepared before users receive them, or run as shared kiosk devices? That needs classic Autopilot's pre-provisioned or self-deploying mode.
- Is any device in the rollout still on Windows 10? Device preparation needs Windows 11.
If the answer to all three is no, Autopilot device preparation offers a simpler set-up, no hardware hash registration and near real-time reporting.
Microsoft recommends deploying new devices as cloud-native using Microsoft Entra join rather than hybrid join. Both solutions can run side by side in one tenant, but each device uses only one of them. If a registered device should use device preparation instead, it must be deregistered first.
Windows 10 matters here too. Microsoft ended Windows 10 support on 14 October 2025, so any rollout still mixing Windows 10 devices is worth reviewing on security grounds as well as deployment ones.
Where Autopilot Still Leaves Work for Your Team
Autopilot automates software setup. It does not remove the operational load around it:
- Registration gaps. Devices bought outside a participating reseller, or moved between tenants, need hashes captured or ownership released.
- Hardware repairs. Microsoft notes that a large hardware change such as a motherboard replacement means a new hash has to be generated and uploaded.
- Physical handling. Unboxing, checks, asset tagging, peripherals, packaging and tracked delivery to homes and sites.
- Records. Knowing which serial number went to which person, and when, for the asset register and later recovery.
- The exit. When a device is retired, it must be deleted from Intune and deregistered from Autopilot before resale, or the next owner inherits your tenant's settings. We cover this in how to sell old business laptops.
For MSPs, this is where margin disappears. The Intune configuration is skilled, billable work. The unboxing and shipping around it is not.
Frequently Asked Questions
Is Windows Autopilot free?
Autopilot is a feature of Microsoft's management stack rather than a separate product, but it relies on licensing such as Microsoft Intune and Microsoft Entra ID. Check your Microsoft 365 plan for what is included.
What is the difference between Autopilot and Autopilot device preparation?
Classic Autopilot requires device registration and supports more scenarios, including pre-provisioning, hybrid join and Windows 10. Device preparation needs no registration, supports Windows 11 and Entra join only, and offers simpler set-up with near real-time reporting.
What was Autopilot white glove?
White glove was the earlier name for Autopilot pre-provisioning, where a technician installs device-targeted apps and policies before the device reaches the user.
Does Autopilot pre-provisioning need TPM 2.0?
Yes. Microsoft lists TPM 2.0 with device attestation as a requirement, because the technician phase uses self-deploying capabilities. Virtual machines are not supported.
Pair Autopilot With a Deployment Partner
The strongest rollouts split the work cleanly. Your IT team or MSP owns the Intune and Autopilot configuration. A deployment partner handles the hardware: receiving, staging, configuration and software imaging to your specification, asset tagging, packaging and tracked delivery, with a record of every device.
Canopy's Deploy service is built to sit alongside your IT team or MSP, not replace them. When devices need fixing later, Repair keeps them in service, and when they retire, Recover handles erasure and resale, and flags any device still tied to your tenant. Our device lifecycle management guide shows how the stages connect.
Take the hardware work out of your next rollout.
Use the form on this page to talk to the Canopy team about staging and deploying your next fleet.